As AI becomes embedded in core business operations, CISOs are confronting a class of risks traditional security models were never built to handle - AI-powered attacks, data exposure, shadow AI, governance gaps, and expanding third-party dependencies. The mandate is no longer just defense. Today's CISO is expected to build trust in AI adoption, hold the line on data and access control, and ensure the organization can respond fast when threats evolve faster than playbooks can.
The leadership conversation aims to explore how artificial intelligence can be leveraged to build a robust security posture - examining both its capabilities and limitations - while equipping security leaders with the strategies and tools needed to develop offensive security frameworks that defend organizations against adversarial threats.
The offsite brings security leaders together to exchange real-world perspective on the risks AI is creating - and the practical steps to stay ahead of them. Expect candid peer insight on balancing innovation with control, resilience, and governance in a landscape that won't slow down to accommodate old models.
Join us for a leadership-level conversation on how security can enable innovation - not stand in its way.
Understand emerging risks from AI-powered attacks, shadow AI and data exposure.
Build stronger controls around data, access, AI adoption and compliance.
Learn from real-world experiences, practical case studies and proven strategies.
Connect with 150+ CISOs, security heads and senior decision-makers.
Leadership insights, peer conversations and meaningful networking
All in one place.
Senior Cyber Security Leaders
Industry Speakers
Insightful Sessions
Panel Discussions
Keynotes
Networking Opportunities
Showcase
CISO Awards Ceremony


Executive Director
Securities & Exchange Board of India (SEBI)
View LinkedIn
Explore how AI is reshaping the role, priorities and responsibilities of modern security leaders.
Hear practical perspectives on building the right controls while enabling responsible AI adoption.
Discuss shadow AI, data exposure, third-party risk and cyber-readiness challenges with fellow leaders.
Gain actionable insights for connecting cybersecurity strategy with resilience, growth and enterprise objectives.
Two days of leadership conversations, strategic insights, peer exchange and meaningful networking.
Delegates arrive, check in and network over lunch.
Unwind to Get Ready for the sessions
As artificial intelligence transitions from experimental technology to the core operating engine of modern enterprises, executive leadership demands a fundamental shift. The traditional mandate of defense and friction-heavy risk mitigation no longer scales against the speed of AI adoption.
Today’s security leaders must balance innovation with resilient control, holding the line on data integrity and third-party dependencies while empowering the business to innovate rapidly and safely.
This keynote explores the cultural, organizational, and strategic transformation required of contemporary CISOs to foster trust, command cross-functional influence across the executive suite, and guide their organizations securely into the AI era.
AI hasn't just changed what enterprises can build — it's changed how fast attackers can move. This session examines how CISOs are preparing for AI-augmented attacks, expanding third-party dependencies, and incident response cycles that now unfold in minutes, not days.
AI agents are changing how enterprises interact with SaaS — moving from users manually operating applications to agents that can access data, make decisions and take actions on their behalf. This shift creates new questions around identity, access, data exposure, governance and accountability. This session explores how security leaders can manage agentic access without slowing down enterprise productivity.
As AI moves into critical enterprise workflows, security teams need to test these systems before attackers do. This session explores how CISOs can adopt an offensive mindset to identify weaknesses in AI models, applications and agentic workflows — and turn those findings into stronger security controls.
A hands-on, practitioner-led format designed to tackle most pressing challenges confronting the security leaders through AI, head-on. Delegates roll up their sleeves and work through real problem statements.
The room is set up as a series of intimate roundtables — think 5 tables, 10 delegates each, in a relaxed café-style setting. Each sponsor is assigned a pre-determined theme and rotates across groups in 30-minute focused sessions, engaging directly with practitioners to surface pain points, stress-test ideas, and co-develop solution approaches. It is one of the most effective formats for sponsors to build genuine credibility with a senior, decision-ready audience.
As enterprises scale artificial intelligence across operational and security workflows, fragmented tooling often introduces blind spots, governance gaps, and integration friction. This session explores how adopting a unified platform consolidation strategy embeds security directly into the AI lifecycle from day one.
As organizations integrate generative and agentic AI into mission-critical workflows, novel attack vectors are challenging traditional cybersecurity models. Adversaries actively target the AI layer through manipulative prompt injections, corrupted training pipelines via data poisoning, and unauthorized employee adoption of unsanctioned AI tools.
The convergence of generative AI and autonomous tooling has fundamentally altered the adversary playbook, enabling attackers to launch polymorphic, hyper-personalized campaigns that iterate and scale in minutes rather than days. When threat actors operate at algorithmic velocity, traditional human-in-the-loop detection models and legacy playbooks become critical liabilities.
 Yoga
 Cycling
 Golf

A luxury retreat designed for strategic conversations, premium networking, and high-impact leadership experiences.
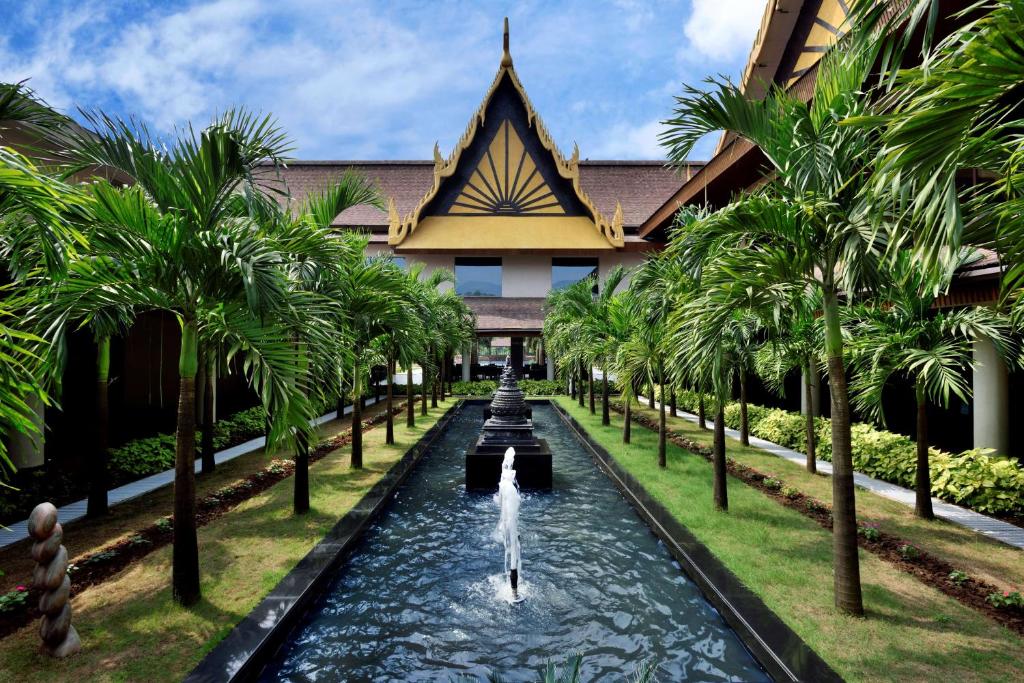
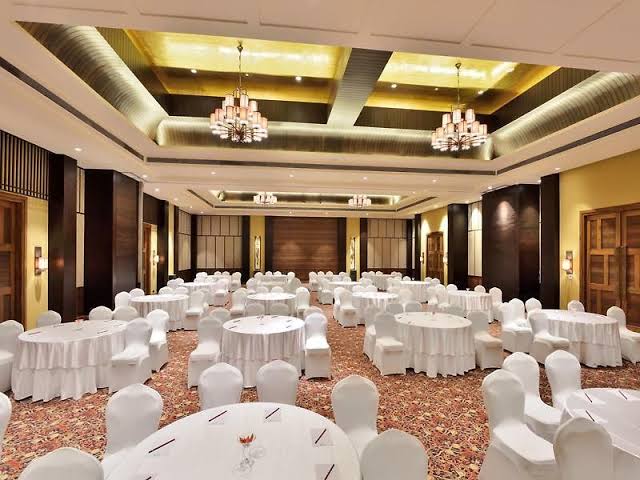
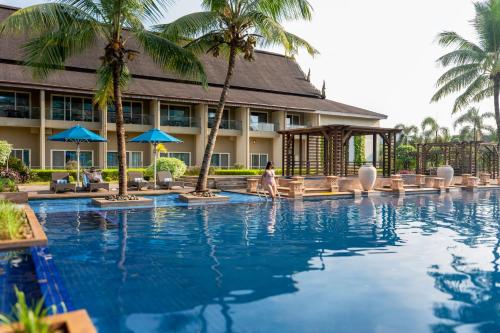
The venue creates the perfect environment for senior leaders to step away from everyday boardroom noise and engage in meaningful, focused conversations.